A working IPv6 guest network for the UniFi ecosystem
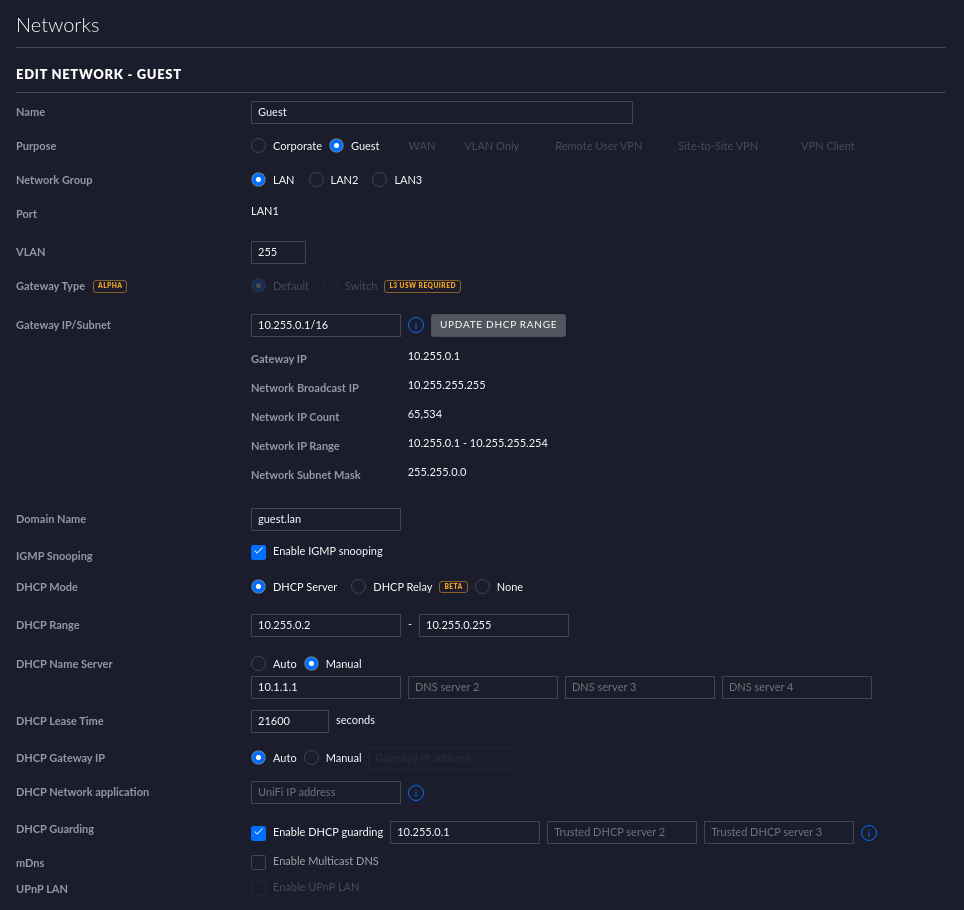
Motivation The number of forum entries on the Internet suggests that IPv6 and UniFi are like fire and water. While corporate networks can be configured without any problems, the implementation for guest networks seems more or less broken. After several attempts and more than a year of research, I found a solution for my setup at home. Caveat The setup does not cover a functional "Guest Portal". Since it is not necessary for my home network, I have not bothered with it. If you require this feature for your network, please treat this guide with caution. My environment I operate a Controller (Build: atag_7.0.22_17284) on a Raspberry Pi 4, a USG Pro 4, a USW 24 PoE and some UAP AC Pro distributed in the house. The wired part A configured guest network for the wired network is required. Here's how I did. My guest network covers the subnet 10.255.0.1/16 for IPv4 and XXXX:XXXX:XXXX:XXXX::1/64 for IPv6 (masked). The DNS entries (DHCP name server) point to my Pi-Hole. You ...